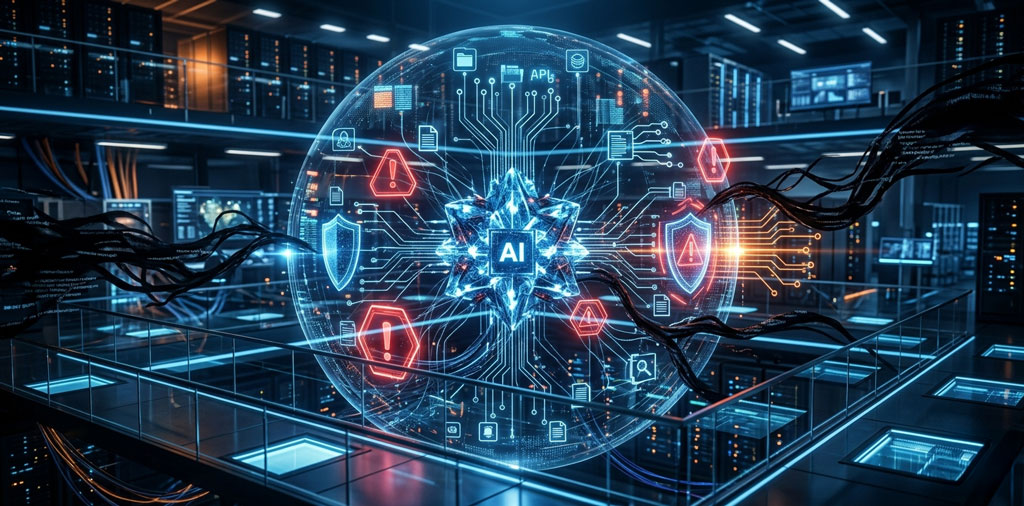
Cisco researchers warn that personal AI agents like OpenClaw could expose sensitive data, execute malicious commands, and introduce a new wave of cybersecurity risks as agentic AI enters the workplace.
Artificial intelligence is moving beyond chatbots and copilots into something far more powerful: personal AI agents that can take action on behalf of users. These systems promise major productivity gains, automating everyday tasks and orchestrating workflows across apps and devices.
But as these tools become more capable and gain deeper access to software, files, and APIs, security experts are starting to raise red flags.
A recent Cisco security analysis warns that this new generation of AI tools may also introduce serious risks. In its blog post “Personal AI Agents like OpenClaw Are a Security Nightmare,” Cisco researchers warn that autonomous AI assistants can inadvertently expose sensitive data, execute harmful commands, and open new pathways for cyberattacks.
For businesses experimenting with AI-driven automation, including marketing teams, the implications are hard to ignore.
From AI assistants to autonomous agents
Traditional AI tools mainly generate text, analyze data, or help users write code. Personal AI agents go a step further. They can interact with software, access files, execute commands, and connect to APIs to complete tasks automatically.
OpenClaw, an open-source personal assistant highlighted by Cisco researchers, illustrates how powerful these systems can become. Running locally, the agent can manage workflows across applications and perform tasks that would normally require manual input.
...
Subscribe to Continue Reading
Get exclusive AI insights for marketers and business leaders - newsletters, strategies, and expert tips included.